Infrequent code integration is a common bottleneck in software delivery. When developers merge large batches of changes at once, integration conflicts multiply and defects surface late in the release cycle. Continuous integration and continuous delivery (CI/CD) reduces these problems by automating the build, test, and release stages that follow a code commit. Each change goes through the same repeatable process as soon as it is committed, reducing reliance on slow manual release steps.
This article explains what CI/CD is, how it works, and how to build, secure, and streamline a pipeline.
What Is CI/CD?
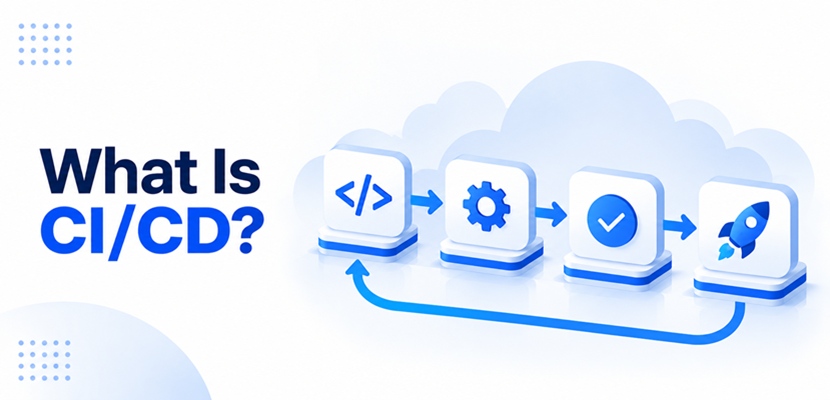
CI/CD is a set of practices that automates how code changes move from a developer's machine to production. Continuous integration (CI) covers merging and testing code, while continuous delivery (CD) covers preparing tested code for release. The CD can also stand for continuous deployment, depending on whether someone approves the final release.
For example, a developer pushes a change to a shared Git repository. A CI/CD tool such as Jenkins detects the commit, builds the application, and runs automated tests against it. If every test passes, the tool packages the build and delivers it to a staging environment, ready for release.
CI/CD sits inside the broader software development life cycle and automates its build, test, and release phases. Planning, design, and requirements work stay outside its scope.
CI/CD Components
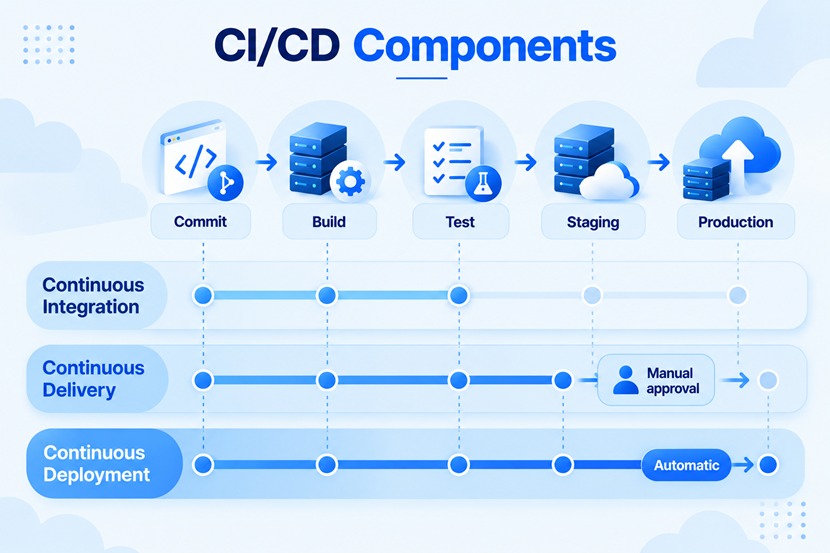
Three related practices make up CI/CD: continuous integration, delivery, and deployment. Each one handles a different part of the release process and builds on the previous one, so adoption follows the same order.
The three practices divide the work as follows:
- Continuous integration. Covers each code commit and the automated build and test stages that follow it, keeping a shared codebase healthy while developers change it.
- Continuous delivery. Extends the pipeline to deploy each tested build to the staging environment, with a manual approval before each release to production.
- Continuous deployment. Extends delivery by releasing every change that passes the automated checks to the production environment without manual approval.
Continuous integration and continuous delivery form the core of a CI/CD setup, while continuous deployment is an optional extension for projects with enough test coverage for changes to be released without manual approval.
Continuous Integration (CI)
The practice of merging code changes into a shared repository several times a day. is called continuous integration. Each merge triggers an automated build and a test suite. Developers get feedback within minutes of pushing a change.
Small, frequent merges keep conflicts manageable. When two developers change the same code, they find out the same day instead of weeks later at release time.
Automated testing is what makes CI reliable. Running tests on every change, a practice known as continuous testing, catches regressions before they spread into other developers' work. The pipeline starts with fast checks, such as unit tests, and runs slower checks in later stages.
Continuous Delivery (CD)
Continuous delivery is the practice of keeping every integrated change ready for a production release. The pipeline packages every change that passes integration and testing into a release candidate and deploys it automatically to test environments, such as staging. This keeps the code in a releasable state at all times.
The production release remains a business decision. A release manager approves the release, and the pipeline carries it out with the same automated steps it used for every earlier environment. Releasing becomes a routine action instead of a planned event.
Continuous Delivery vs. Continuous Deployment
Both practices automate every step before production and differ in how the release itself happens. Continuous delivery requires a person to approve each production release.
Continuous deployment removes that approval step, and any change that passes the automated checks goes live without human intervention. It depends on a high level of trust in automated testing, since no one reviews the release before users see the change. Organizations that adopt it also add safeguards such as automatic rollback and feature flags, which switch new code on or off without a new deployment. Continuous delivery suits organizations that want control over when a release goes live, such as to coincide with a product launch or to follow a formal change approval process.
How Does CI/CD Work?
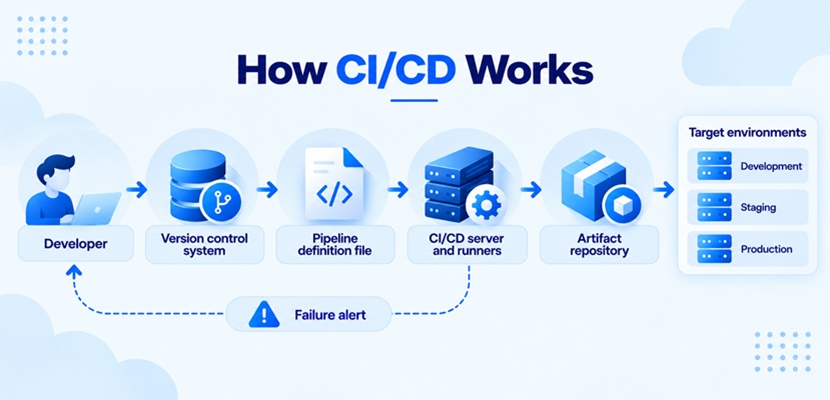
An automated CI/CD workflow relies on several connected systems that pass each code change from one step to the next. A developer interacts directly with only one of them – the version control system. Everything after the commit happens automatically, driven by rules stored in the repository alongside the code.
The main systems involved in CI/CD are:
- Version control system. Stores the source code and its full change history, most often in Git. A commit or merge request to the repository triggers the pipeline.
- Pipeline definition file. Describes each job, the order of the jobs, and the conditions for running them. The file lives in the repository as a configuration file, so reviewers check pipeline changes like any other code.
- CI/CD server and runners. Handles job orchestration and execution. The server assigns each job to a runner, also called an agent, which is a machine or container that performs the work.
- Artifact repository. Holds the built output, such as a container image or a software package. Later stages pull from the artifact repository, so every environment receives the exact same build.
- Target environments. Receive the build in sequence, from the development environment through staging to the production environment. Each environment tests the build under conditions closer to live use.
Notifications connect these systems together. When a job fails, the server stops the pipeline and alerts the developer who made the change via chat, email, or the merge request itself. The failed change goes no further until someone fixes it.
The CI/CD Pipeline
A CI/CD pipeline is the ordered sequence of stages every code change passes through on its way to production. Each stage acts as a gate. A change moves forward only after it passes the current stage, so problems are caught as early as possible.
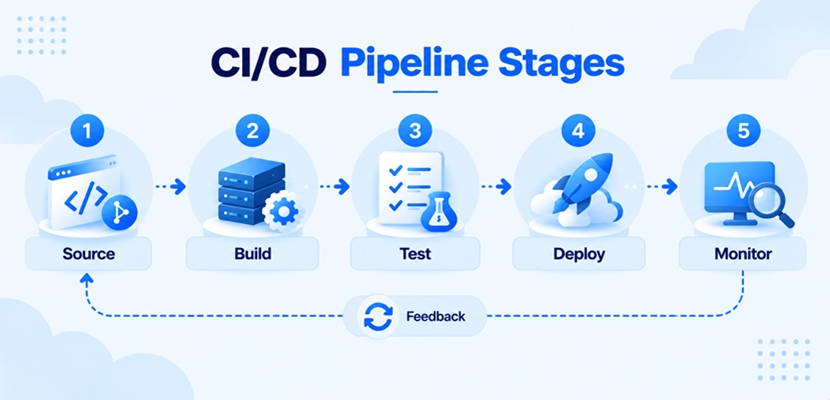
A standard pipeline consists of the following stages:
- Source. A commit or merge request to the repository starts the pipeline. Some pipelines also run on a schedule or on manual request.
- Build. The pipeline compiles the code, resolves its dependencies, and packages the result into a deployable artifact. A failed build stops the pipeline immediately.
- Test. Automated tests, ordered from fastest to slowest, verify the build. Unit tests and static code analysis run first. Integration tests, functional tests, and automated security testing follow once the fast checks pass.
- Deploy. The pipeline releases the artifact to the staging environment and then to the production environment, either after approval or automatically.
- Monitor. Application monitoring tools track errors and performance after the release. A sharp rise in errors can trigger an automatic rollback, and monitoring findings feed back into the next code change.
The test stage varies the most between pipelines, since each application needs a different mix of test types. Many pipelines also include stages for manual approvals, database migrations, or compliance checks.
CI/CD Principles
Pipelines and tools differ from one project to another, but the rules behind them stay the same. Each rule serves the same goal: getting every change to production quickly and safely.
The core CI/CD principles are:
- Commit small changes often. Developers merge work into the main branch at least daily. Short-lived branches keep conflicts small, and some projects commit straight to the main branch, a model known as trunk-based development.
- Build and test every change. No change reaches the main branch without passing the automated build and test suite.
- Keep the build fast. Quick feedback keeps developers focused on the change they just made, so slow tests move to later stages instead of blocking every commit.
- Fix broken builds immediately. A failing main branch blocks every developer who depends on it, so repairing it takes priority over new work.
- Keep the main branch releasable. Every commit on the main branch is a potential release, and unfinished features stay hidden behind feature flags.
- Build once, deploy everywhere. The pipeline promotes the same artifact from testing to production. Rebuilding for each environment risks shipping a build that differs from the one that passed the tests.
- Automate every release step. Application automation replaces manual packaging, configuration, and deployment tasks with scripts and pipeline jobs, which makes each release repeatable.
The first four principles belong to continuous integration because they protect the main branch from conflicts and broken builds. The last three belong to continuous delivery because they turn every tested change into a predictable release.
CI/CD Benefits
Applying IT automation to software delivery is more than accelerating the process. It also affects how developers find bugs, share information, and plan their work. Most of the gains trace back to one change: small, frequent releases instead of large, infrequent ones.
The main CI/CD benefits include:
- Faster releases. Changes reach users as soon as they pass the pipeline, without waiting for a scheduled release window.
- Earlier bug detection. Tests run on every commit, so bugs surface while the code is fresh and cheaper to fix.
- Lower release risk. Each release contains only a few changes, which makes a failure easy to trace and roll back.
- Faster feedback. Developers learn quickly whether a change works, and frequent releases bring user feedback sooner.
- Greater visibility. Every build, test result, and deployment leaves a record that shows where the process slows down.
- Less manual work. Developers and operations staff spend less time on repetitive build and release tasks and more time on product work.
The gains depend on test quality. A pipeline with weak tests will only ship bugs faster, making the choice of test suite central to any CI/CD setup.
CI/CD Tools
A CI/CD tool reads the pipeline definition, runs the jobs, and reports the results. Options range from self-hosted servers to fully managed services. Some setups combine a CI tool with a separate deployment tool.
Widely used CI/CD tools include:
- Jenkins. An open-source automation server with a large plugin ecosystem, suited to users who want full control over a self-hosted setup.
- GitHub Actions. A CI/CD service built into GitHub that runs workflows defined in files stored in the repository.
- GitLab CI/CD. A pipeline feature built into the GitLab platform, available as a managed service or a self-hosted installation.
- CircleCI. A cloud-based CI/CD service focused on fast, parallel builds, with the option to run jobs on self-hosted runners.
- TeamCity. A build server from JetBrains with both cloud and on-premises editions.
- Argo CD. An open-source deployment tool for Kubernetes that keeps a cluster in sync with the configuration stored in Git, an approach known as GitOps.
Most pipelines also rely on DevOps tools outside the CI/CD category, including container platforms, infrastructure provisioning tools, and monitoring systems.
CI/CD and DevOps
DevOps is a culture and operating model that brings development and operations teams together around shared responsibility for software. CI/CD applies that model to software delivery. DevOps principles define how people collaborate, and CI/CD provides the automated workflow that makes frequent, reliable releases possible.
The relationship works in both directions. A CI/CD pipeline without DevOps culture often stalls, since developers and operations engineers still work in separate groups and dispute ownership of failures. DevOps without CI/CD lacks the automation to release changes at the pace the culture aims for.
Two related concepts build on the same foundation. A DevOps pipeline wraps planning, operations, and feedback phases around the CI/CD core. DevSecOps adds security to the model, running checks such as dependency scanning and secret detection as pipeline stages so they apply to every change automatically.
How to Build a CI/CD Pipeline
Building a CI/CD pipeline is an incremental project. Most organizations start by automating the build and a few tests for one application, then add stages once the initial pipeline runs reliably. Starting small also shows which parts of the existing release process cause the most delays.
1. Map the Current Release Process
Document every step between a finished code change and a production release, including manual approvals, scripts, and handoffs between departments. Note which steps take the longest and which fail most often, since they are the first candidates for automation. Pick one actively developed application as the pilot project.
2. Set Up Version Control and a Branching Strategy
Place the application code, build scripts, and configuration in a single version control system, and agree on a branching strategy for merging work. Trunk-based development and short-lived feature branches both suit CI, while long-running branches delay integration. Require a peer code review on every merge request so a second developer checks each change before it reaches the main branch.
3. Choose a Tool and Define the Pipeline as Code
Select a CI/CD tool that integrates with the version control system and supports the project's languages and deployment targets. Write the pipeline definition as a file in the repository instead of configuring it through a web interface. Pipeline as code keeps the pipeline versioned, reviewable, and easy to recreate if the CI/CD server fails.
4. Automate the Build and Tests
Configure the pipeline to build the application on every commit and store the output in an artifact repository. Add tests in layers, with fast unit tests and static analysis first and slower integration tests later. Established test automation frameworks give the test suite a consistent structure, removing the need for custom tooling.
5. Provision Consistent Environments
Define test, staging, and production environments with infrastructure as code (IaC). Building every environment from the same templates removes the configuration differences that let code pass testing and then fail in production. Infrastructure automation also lets the pipeline create short-lived test environments on demand and remove them after each run.
Decide where the runners operate as well. Managed runners from the tool vendor need no maintenance, while self-hosted runners on an organization's own servers offer more control over performance, hardware, and network access. Server automation keeps those machines patched and consistently configured.
Note: phoenixNAP's Bare Metal Cloud (BMC) is a dedicated server with the flexibility of the cloud. Its IaC integrations let a CI/CD pipeline provision infrastructure with Terraform or the BMC Ansible module, so self-hosted runners and test environments run on dedicated hardware.
6. Automate Deployment and Monitoring
Script the deployment to each environment so every release follows the same steps. The release strategy then determines how the new version replaces the old one and how many users a failed release affects.
Common release strategies include:
- Blue-green deployment. Runs the new version alongside the old one and switches traffic once the new version is healthy.
- Canary release. Sends the new version to a small share of users first and expands the rollout only if error rates stay normal.
- Rolling deployment. Replaces instances of the old version with the new one in batches, so part of the application stays available throughout the update.
- Dark launch. Ships new code to production in a disabled state and enables it for selected users later through feature flags.
Connect monitoring to the pipeline so a rise in errors after a release triggers an alert or an automatic rollback. At first, require manual approval before each production release. Move to continuous deployment once the test suite proves reliable.
CI/CD Challenges and Limitations
Automating releases removes manual work, but it adds a system that needs its own design, maintenance, and protection. The problems below appear most often as pipelines grow in size and importance. Some are technical, while others come from organizational habits.
The most common CI/CD challenges include:
- Flaky tests. Tests that pass and fail at random erode trust in the pipeline. Developers start rerunning failed jobs or ignoring results, which lets actual bugs through.
- Slow pipelines. Build and test times grow with the codebase. Long waits push developers back toward large, infrequent merges.
- Pipeline security. A pipeline holds credentials for repositories, artifact registries, and production systems, which makes CI/CD security a priority. Compromised third-party plugins and actions have already exposed secrets from the build logs of widely used projects.
- Legacy applications. Applications with a monolithic application architecture, manual setup steps, and few tests are hard to automate. Adding CI/CD often requires refactoring and writing tests first.
- Cultural resistance. Frequent small merges and shared ownership of the main branch change how developers work. Developers used to long feature branches and release freezes need time to adjust.
- Maintenance overhead. Pipelines, runners, and environments need updates like any other system. Without a clear owner, pipeline configurations can drift out of date and break.
These challenges are manageable and outweighed by the value of automated delivery. The longer they go unaddressed, the longer they take to fix, making routine pipeline maintenance part of the job.
CI/CD Best Practices
Ongoing maintenance keeps a CI/CD pipeline fast and secure. Consistent practices for credentials, testing, and measurement keep an existing setup reliable as the codebase grows.
The core CI/CD best practices are:
- Protect secrets. Store credentials in a dedicated secrets manager or the tool's encrypted store, never in the repository or the pipeline file. Rotate them on a regular schedule.
- Apply the principle of least privilege. Give each pipeline job only the permissions it needs, so a compromised job cannot reach systems outside its scope.
- Pin third-party dependencies. Reference plugins, actions, and libraries by a fixed version or commit hash so an upstream change cannot alter the pipeline without review.
- Treat flaky tests as bugs. Fix or quarantine unreliable tests quickly instead of rerunning jobs until they pass.
- Cache and parallelize. Reuse dependencies between runs and split large test suites across runners to keep feedback fast.
- Standardize pipelines across projects. Share reusable pipeline templates so every project follows the same build, test, and security steps.
- Measure delivery performance. The DevOps Research and Assessment (DORA) program defines five DevOps metrics for delivery speed and stability, including deployment frequency, change lead time, and change failure rate.
Security deserves the most attention on this list. A pipeline with access to production is part of the production attack surface and needs the same controls as any other critical system.
Making CI/CD Part of Everyday Development
CI/CD gives every code change the same short, automated path from commit to production. The results depend on consistency: small changes, trustworthy tests, and fast feedback. Start with one application, automate its build and tests, and add delivery stages as the results prove reliable.